




New to KubeVault? Please start here.
Overview
The KubeVault operator makes it easy to deploy, maintain and manage Vault servers in Kubernetes clusters. It covers automatic initialization and unsealing and also stores unseal keys and root token in a secure way. The KubeVault operator can manage policies and secret engines of Vault servers which are not provisioned by the KubeVault operator. It has the following features:
Vault Policy Management: Provides a Kubernetes native way to manage Vault policies and bind those policies to the users or the auth method roles.
Vault Secret Engine Management: Provides a Kubernetes native way to manage Vault secret engines.
- AWS Secret Engine
- Azure Secret Engine
- Database Secret Engine
- Druid Secret Engine
- Elasticsearch Secret Engine
- etcd Secret Engine
- Ignite Secret Engine
- Kafka Secret Engine
- MariaDB Secret Engine
- Microsoft SQL Server Secret Engine
- Milvus Secret Engine
- MongoDB Secret Engine
- MySQL Secret Engine
- Neo4j Secret Engine
- Oracle Secret Engine
- PostgreSQL Secret Engine
- Qdrant Secret Engine
- RabbitMQ Secret Engine
- Redis Secret Engine
- SAP HanaDB Secret Engine
- Solr Secret Engine
- Weaviate Secret Engine
- GCP Secret Engine
- Key/Value Secret Engine
- PKI Secret Engine
Setup Vault Server
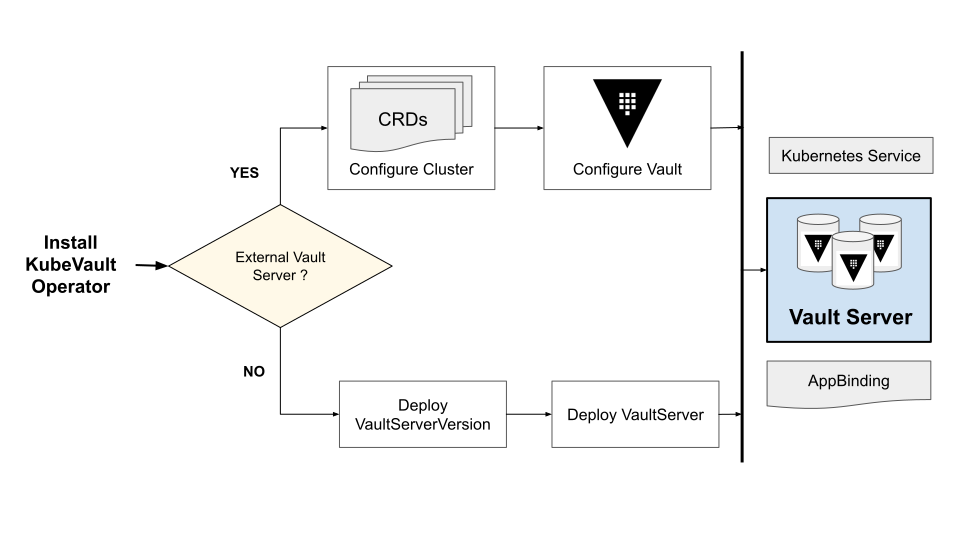
Deploy Vault server using the KubeVault operator:
Configure external Vault server so that the KubeVault operator can communicate with it: